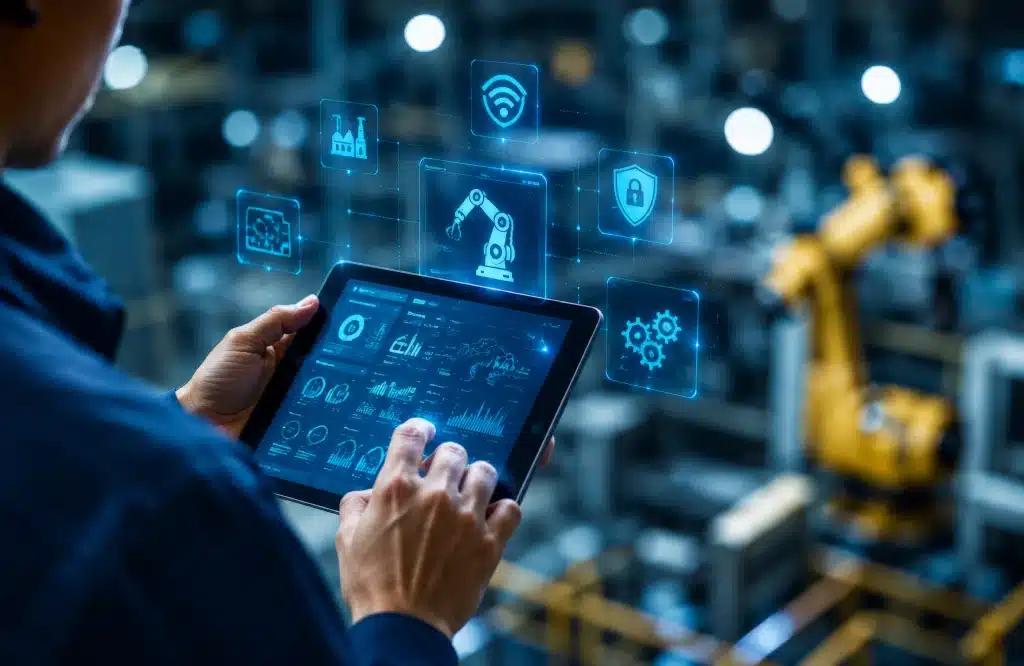
Manufacturing environments are becoming more connected, but that connectivity also makes cybersecurity more complicated. Business systems, production equipment, sensors, and industrial controls increasingly exchange data, creating more opportunities for an attack in one part of the organization to affect another.
These connected systems generally fall into two categories: information technology (IT), which supports business data and applications, and operational technology (OT), which controls or monitors physical equipment and production processes. Because the two environments serve different purposes, they cannot always be secured in the same way. Understanding those differences is essential to reducing cyber risk across a manufacturing operation.
IT and OT serve different purposes
Information technology (IT) covers the technology employees use to store, process, and share business information. Email accounts, laptops, servers, and enterprise resource planning software belong to the IT environment. Security controls typically focus on preventing unauthorized access and protecting sensitive data.
Operational technology (OT) includes the equipment and software that monitor or control physical processes. In a manufacturing facility, OT can include assembly line controls, robotic equipment, temperature and pressure sensors, and computerized machinery used in production.
The distinction matters because an IT outage may prevent employees from accessing files, while an OT incident can stop a production line or affect physical equipment. In OT environments, availability and safe operation often take priority. However, OT performance and safety requirements affect cybersecurity decisions.
Connected systems create shared exposure
IT and OT once operated as largely separate environments. Modern manufacturing has changed that. Production equipment may now exchange information with inventory platforms, cloud applications, and other business systems, while equipment vendors may connect remotely for maintenance and support.
These connections make manufacturing operations more efficient, but they also allow security problems to cross between environments. An attacker who compromises an employee account or office computer may be able to move toward production systems if the networks are not properly separated.
Manufacturers therefore need to understand not only how IT and OT differ, but also how the two environments interact. A network security audit can identify unnecessary connections, outdated access rules, and other weaknesses that could allow a threat to move between business and production systems.
Why OT security requires a different approach
Standard IT practices do not always translate neatly to the production floor. An office computer can often be restarted after a software update with little consequence. Taking a control system offline, however, could interrupt production or affect equipment safety.
OT environments may also contain specialized machinery that remains in service for many years. Some systems rely on older software that cannot be easily updated or replaced, making standard patching schedules impractical.
Security decisions around OT must account for how each system affects production. When equipment cannot be patched or replaced immediately, manufacturers may need to reduce exposure through network separation, restricted access, or other safeguards instead.
Build security around operational risk
A coordinated IT and OT security strategy starts with knowing what is connected and how those systems depend on one another. Manufacturers should maintain an accurate inventory of production equipment, connected devices, and the business systems that communicate with them. The inventory should also identify who manages each asset and which outside vendors can access it.
Manufacturers can then prioritize several protections:
- Separate business and production networks to restrict unauthorized movement.
- Require multifactor authentication for employees and outside vendors.
- Limit remote access to approved users and defined maintenance periods.
- Monitor network activity for behavior that differs from normal operations.
- Maintain recovery procedures that account for safe equipment restoration.
IT and operations teams need a shared plan
Protecting interconnected environments also requires coordination between the people responsible for them. IT teams understand networks, cyberthreats, and security controls, while operations personnel understand how equipment behaves and what production can safely tolerate.
Effective planning depends on both perspectives. IT and operations teams should work together on risk assessments, security changes, and incident response planning. Their responsibilities should also be clear before an incident occurs, including who has authority to disconnect equipment, how production will continue during an outage, and which systems should be restored first.
Outside vendors should be part of that planning as well when they have remote access to production equipment or play a role in maintenance and recovery.
Protect the connection, not just each side
Manufacturers do not need identical controls across IT and OT. They need a coordinated approach that respects both environments. A professional security assessment helps manufacturers uncover gaps between their business and production networks. The resulting plan should support the factory’s actual equipment and operating requirements rather than force a generic IT model onto the plant floor.
Unsure where the greatest risks lie between your office systems and production equipment? Schedule a consultation to develop an IT and OT security plan that protects operations without placing unnecessary strain on production.